What these numbers count
A record is one post that AdverseMonitor collected from a ransomware leak site, a criminal forum, a Telegram channel or the open web, and that names a victim in the country. We have collected since 20 August 2025. Every count here is a claim made by someone else. We have not confirmed any of them, and the method section at the end lists what that means for the figures.
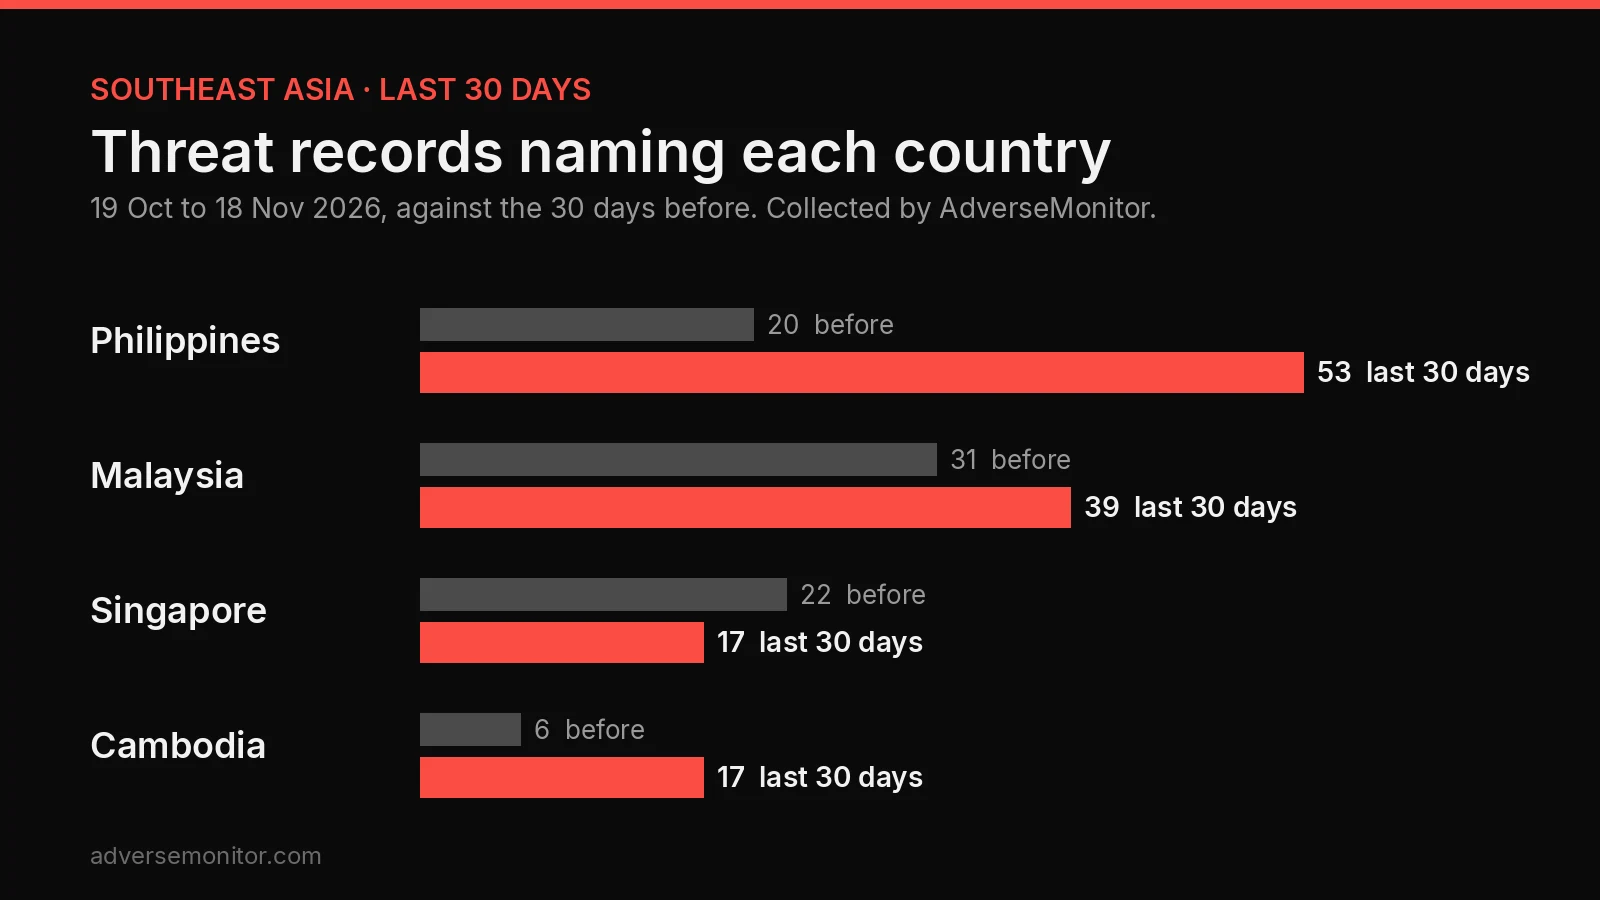
| Country | All records | Last 30 days | 30 days before | Largest category | Most named group |
|---|---|---|---|---|---|
| Malaysia | 312 | 39 | 31 | Ransomware (76) | DeepCore Network (24) |
| Singapore | 190 | 17 | 22 | Ransomware (68) | The Gentlemen (11) |
| Philippines | 314 | 53 | 20 | Data breach (119) | BABAYO EROR SYSTEM and Qilin (16 each) |
| Cambodia | 87 | 17 | 6 | Data breach (25) | NXBB.SEC (9) |
For scale, the same 30 days produced 256 records for Indonesia and 66 for Thailand, so the four countries in this report are smaller targets. Their share is growing, though: the Philippines and Cambodia rose while Indonesia and Thailand fell.
Philippines: breach claims more than doubled
The Philippines had 53 records in the last 30 days, against 20 before. November had 41 by the 18th, already more than any full month since June. Data breach claims lead, with 119 of the 314 records since August 2025, followed by 54 defacements and 44 ransomware posts.
Government administration is named in 71 records and education in 34. BABAYO EROR SYSTEM and Qilin each appear in 16. BABAYO EROR SYSTEM is far busier in Indonesia, with 185 records there, so Philippine targets are a side line for it.
Malaysia: ransomware and network access for sale
Malaysia rose from 31 to 39 records. Ransomware leads with 76 records since August 2025. Close behind are 73 initial-access posts, where a seller offers a way into a company network. Those sales often come before a ransomware attack, so a listing that names your network deserves a look at your VPN and remote-access logins the same day.
Government administration appears in 78 of Malaysia's 312 records, a quarter of the total. DeepCore Network leads the groups with 24 records, then Qilin with 16 and BIGBROTHER with 10. October was the busiest month since June, with 43 records.
Singapore: fewer records, more of them ransomware
Singapore fell from 22 to 17 records. Ransomware makes up 68 of its 190 records, or 36 percent, the highest share of the four countries. IT services firms are named in 17 records and financial services in 12.
The Gentlemen appear in 11 records and Qilin in 10. Nullsec Philippines, a group whose name points elsewhere, appears in 7.
Cambodia: small numbers, sharp rise
Cambodia had 17 records in the last 30 days, against 6 before. The total since August 2025 is 87, mostly data breach claims (25), access sales (17) and DDoS claims (14). Government administration is named in 31.
Several of the groups active in Cambodia are much larger in Thai records. NXBB.SEC has 9 Cambodian records and 157 Thai ones. When a group works across a border like this, a quiet month in one country says little about the next.
Groups that work across the region
Qilin is the one group in the top lists of Malaysia, Singapore and the Philippines, with 42 records across the three. It runs a ransomware leak site and gives each named victim a deadline before it publishes the data. DeepCore Network appears in 24 Malaysian records and 79 Indonesian ones. If you serve customers in more than one of these countries, watch the group, not only the country. Each group has a public page on the AdverseMonitor data pages.
What to do with this
Put the domains and company names you are responsible for into monitoring, then decide who checks each match and how fast. For government agencies, schools and IT service providers in these countries, the records above suggest checking at least daily.
When a match arrives, find out whether the claim is new, whether the sample matches your data, and whether anyone has used the access on offer. Our breach response playbook walks through those checks. MSSPs who run this for several clients can read how the platform handles monitoring for MSSPs, or check a domain now.
Method and limits
Counts come from AdverseMonitor's public country aggregates on 18 November 2026. A record counts for a country when it names a victim there; a record that names two countries counts for both. The last 30 days run from 19 October to 18 November 2026. We count posts, not incidents, so one attack reposted on three sites can appear three times, and an attack nobody posts about does not appear at all. Industry labels come from the record or from our classifier, and some records carry none.